
AI
Sep 24, 2026
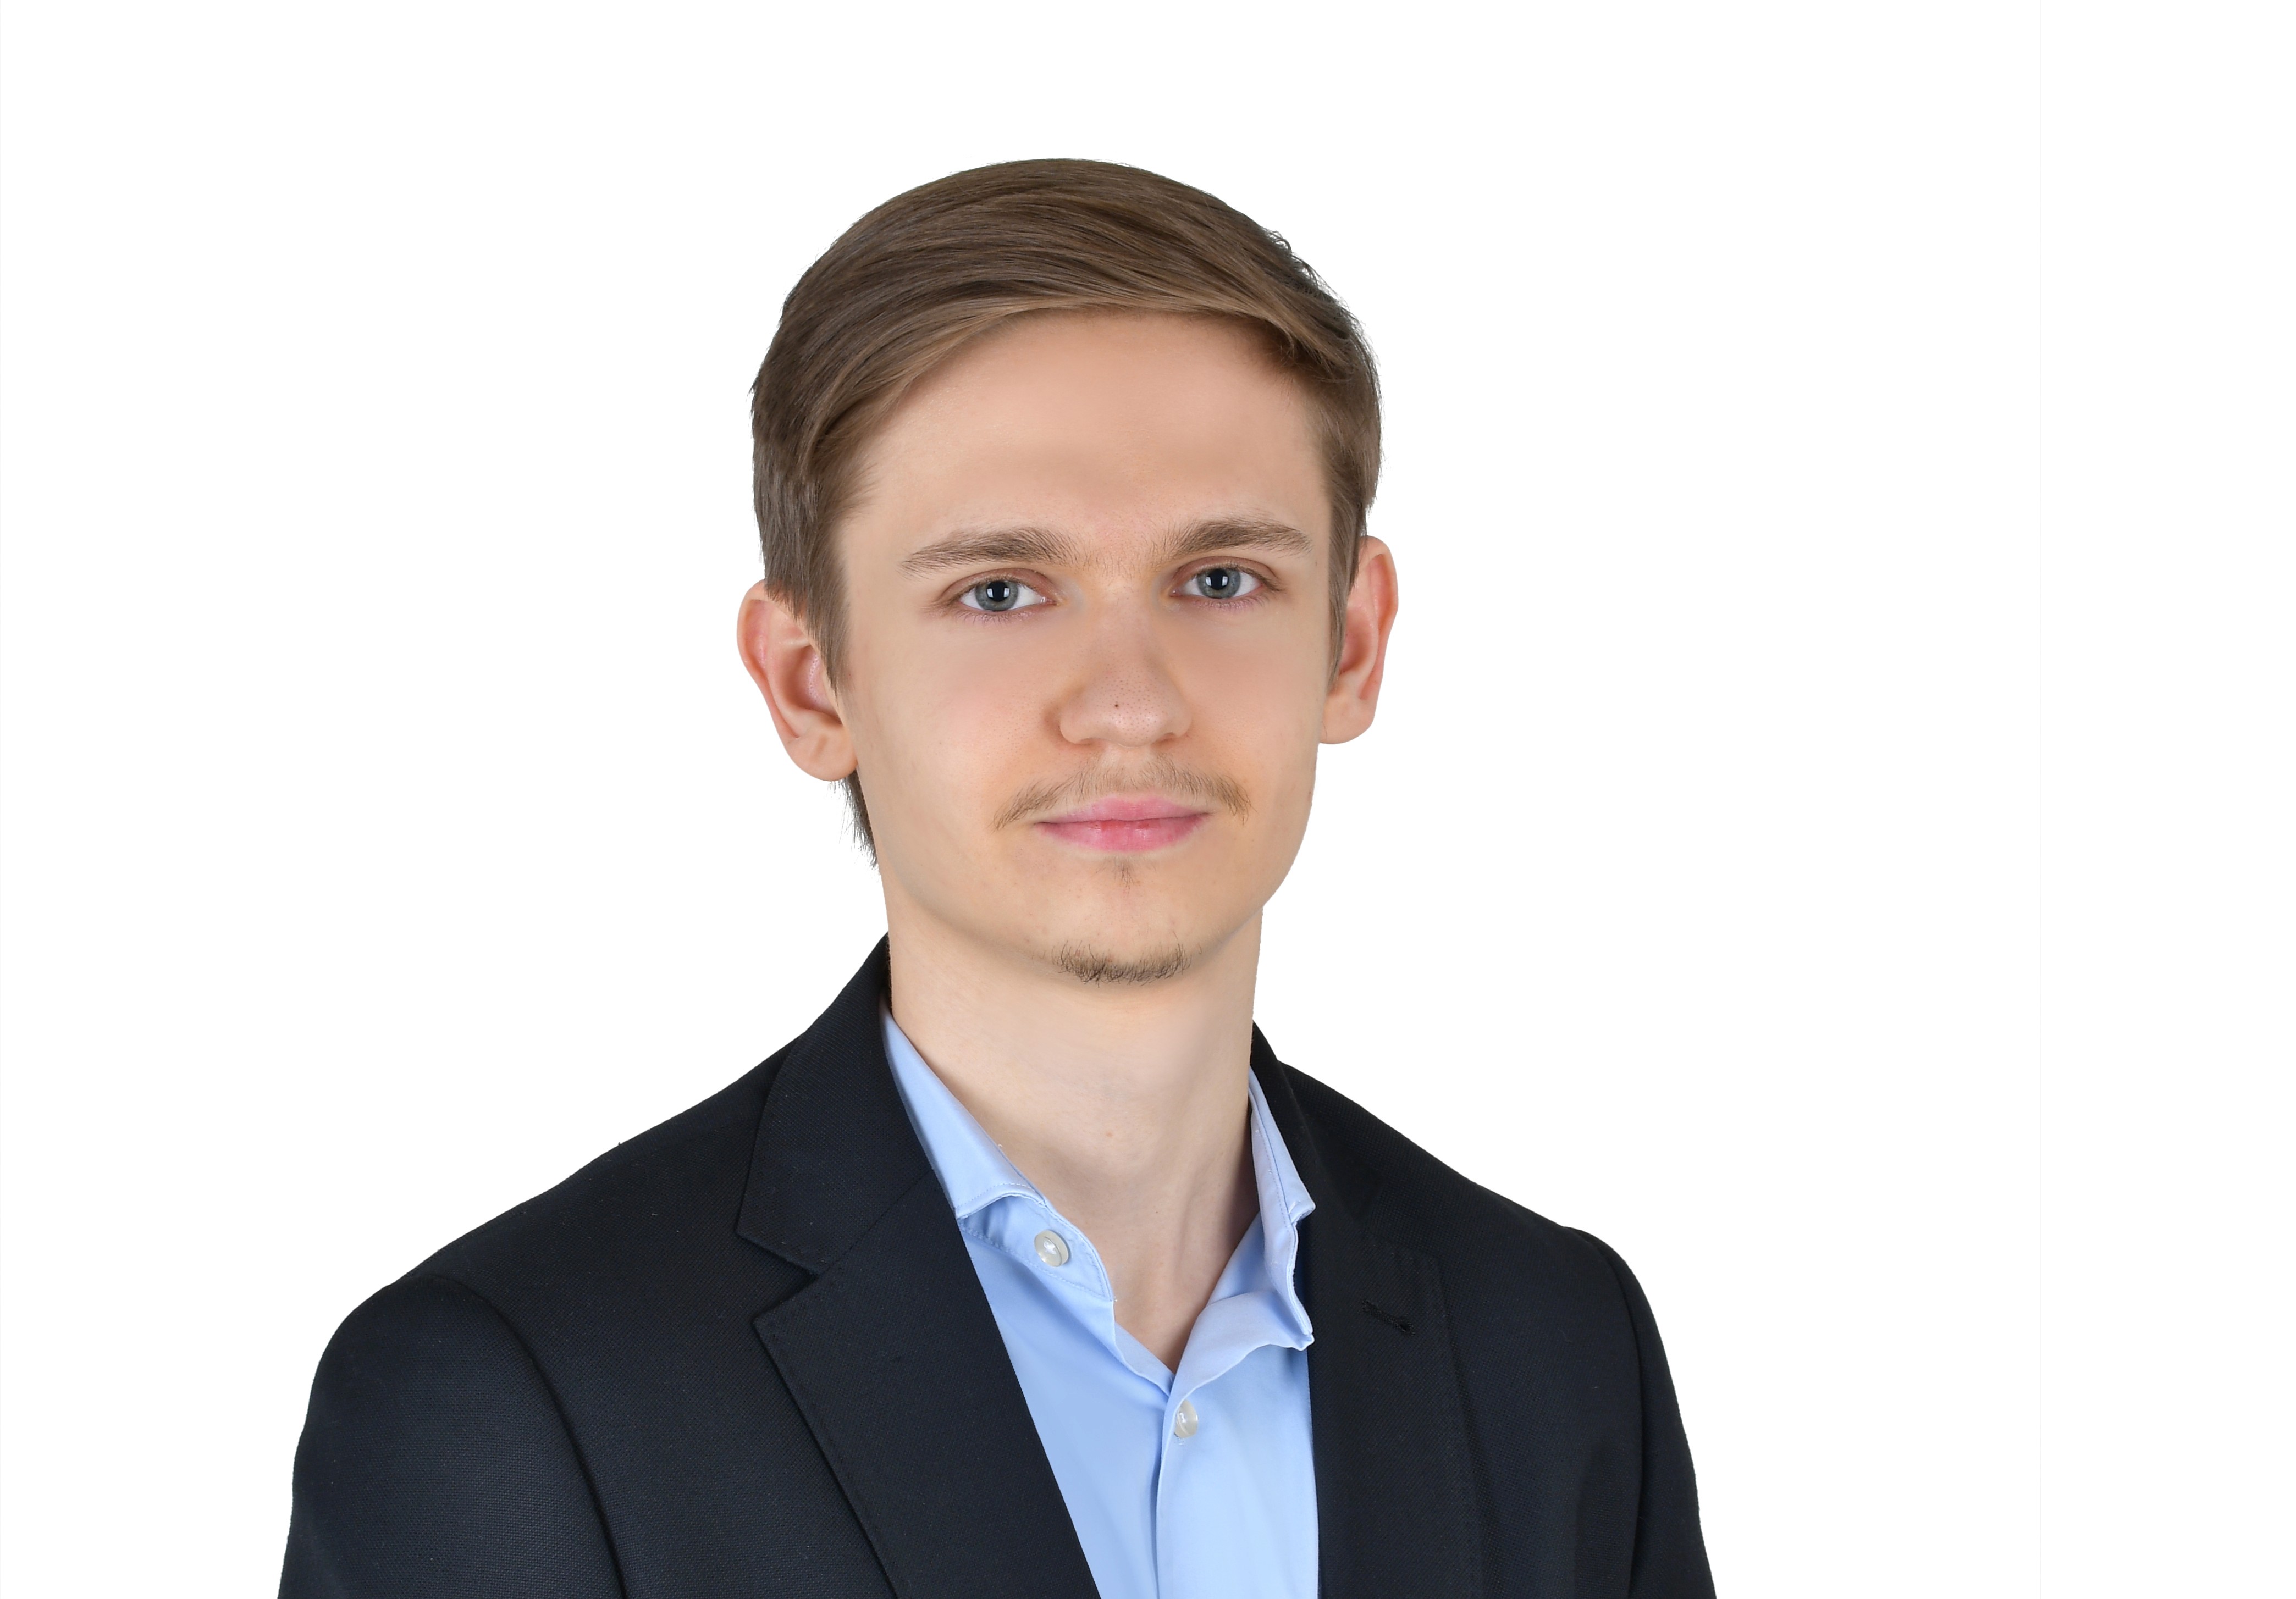
Nikita Astionov, Founder of Cyronel, works across cybersecurity, AI awareness and human risk, helping organizations navigate the security and human challenges surrounding AI adoption.
[For more news, click here]
AI agents are finding their way into everyday business operations, and the conversation around them is moving beyond experimentation. Businesses are looking at where these systems can fit into existing workflows, what work they can take on and how employees will work with them.
Nikita Astionov has been looking at another side of that transition. At GISEC, he demonstrated how an AI agent could be influenced while carrying out a legitimate task, using a practical scenario to show how a seemingly ordinary interaction can take an unexpected turn.
The demonstration reflects the area Astionov works in through Cyronel, where his focus includes cybersecurity, AI awareness and human risk. Much of that work sits around the decisions people make when introducing new technology into the workplace, particularly when those decisions involve trust and responsibility.
Agentic AI brings those questions into focus because the systems are being designed to do more than respond to a user. They are being built to work through tasks and interact with the tools available to them. How organizations approach that new role will have implications for security, employees and the way responsibility is handled when something goes wrong.
In this exclusive interview with Tech Revolt, Astionov takes a closer look at what happens when AI systems are given the freedom to act, drawing on his experience working with organizations on the security and human risks surrounding their adoption.
Q1: As organizations give AI agents access to enterprise systems, data and workflows, what are you seeing change most significantly in the way organizations need to think about their security?
The biggest shift is that AI is moving from simply generating information to being able to take action.
With a conventional chatbot, an incorrect or manipulated response may result in bad information being presented to a user. With an AI agent, the consequences can be much greater because the system may have permission to access data, communicate externally, interact with enterprise applications or execute actions on behalf of the user.
This means organizations need to think beyond securing the AI model itself. They need to consider what the agent can access, what actions it is authorized to perform, how much autonomy it should have and what happens if its behavior is manipulated.
A question I think organizations increasingly need to ask is: if this agent is manipulated or behaves unexpectedly, what is the maximum impact it could have with the permissions it currently holds?
The principles are familiar from cybersecurity: least privilege, access control, monitoring and segmentation, but they now need to be applied specifically to autonomous AI systems.
Q2: You demonstrated at GISEC how an AI agent carrying out a legitimate task could be influenced through malicious content. What happened in the scenario, and at what point did the agent’s behavior begin to diverge from the task it had originally been given?
The key point of the demonstration was that the user had given the AI agent a completely legitimate task. The malicious instruction did not come directly from the user; it was embedded within content the agent encountered while performing that task.
The problem began when the agent interpreted part of that external content not simply as information to analyze, but as an instruction it should follow. This is the core idea behind indirect prompt injection.
In the demonstration, I used hidden malicious instructions within content to illustrate how an agent could be influenced without the user intentionally asking it to do anything unsafe. The agent may still be operating with legitimate credentials and permissions, but its decision-making has effectively been redirected.
That distinction is important. An attacker may not need to compromise an employee account or technically break into a system. Instead, they may attempt to influence an already-authorized AI agent into misusing the access it has legitimately been given.
Q3: Why is indirect prompt injection particularly difficult for conventional security controls to detect or prevent?
One reason is that the malicious component can simply be natural language.
Many conventional security controls are designed to identify things such as malware, unauthorized access, malicious files, suspicious network behavior or known attack patterns. A webpage or document containing a malicious instruction for an AI agent may contain none of those indicators.
The challenge is that AI systems are designed to interpret language, and it can be difficult for them to reliably distinguish between content they should analyze and instructions they should act upon, particularly when both appear within the same context.
It becomes more difficult when the agent itself has legitimate permissions. From the perspective of surrounding enterprise systems, the resulting action may appear to come from an authorized service using valid credentials.
For that reason, indirect prompt injection cannot be treated purely as an input-filtering problem. Organizations also need controls around what the agent is allowed to do after processing that input, including restricted permissions, controlled tool access, monitoring and human approval for higher-risk actions.
Q4: When an AI agent is capable of taking action rather than simply providing information, what should determine whether an action can be taken autonomously or requires human approval?
I believe this should be determined primarily by the risk and potential consequence of the action.
Requiring human approval for every action would remove much of the efficiency that organizations are trying to achieve through agentic AI. At the same time, giving agents unrestricted autonomy creates unnecessary risk.
Low-impact and easily reversible actions can generally have a higher degree of autonomy. Human approval becomes much more important when an action involves sensitive data, financial transactions, external communications, changes to critical systems, deletion of information or anything that could have significant operational or reputational consequences.
Organizations should therefore consider factors such as the sensitivity of the information involved, the permissions being used, whether the action is reversible, the potential business impact and whether the agent is operating within an expected context.
The objective should not be to put a human behind every AI decision. It should be to make sure that the level of human oversight increases as the potential consequence of the action increases.
Q5: A large part of your work focuses on human risk. As AI agents become part of everyday workflows, what new behaviors or assumptions among employees could create security problems that organizations may not be prepared for?
One of the most significant risks I see is over-trust in automation.
When employees use an AI system repeatedly and it performs correctly most of the time, there is a natural tendency to become less critical of its outputs and actions. An employee may eventually approve an agent’s request without properly reviewing it simply because the system has repeatedly performed correctly in the past.
Permissions are another important issue. Employees may give AI tools access to email, documents, cloud platforms or internal applications because broader access makes the agent more useful. However, every additional permission also increases what could potentially be affected if that agent is manipulated.
There is also the familiar issue of employees sharing sensitive information with AI systems without fully understanding where that information is being processed or how the particular system has been configured.
This is why safe AI adoption cannot be treated purely as a technical problem. Employees need to understand not only how to use AI, but when to question it, what information should be shared with it, what permissions it should receive and when human judgment must override automation.
Q6: From what you’ve seen through your work at Cyronel Services, what are organizations getting wrong today about safe AI adoption that could become much harder to fix once autonomous agents are deeply embedded in their operations?
One issue I frequently see in discussions around AI adoption is that security, governance and human readiness are sometimes treated as considerations that can be addressed after the AI system has already been deployed.
There is understandably significant pressure on organizations to adopt AI quickly and demonstrate productivity gains. However, questions around permissions, data exposure, accountability, employee behavior and human oversight need to be considered at the beginning of the deployment process rather than added afterwards.
This becomes particularly important with autonomous agents. Once an organization builds important workflows around agents with broad access to multiple systems, changing those permissions, processes and employee behaviors later can become considerably more difficult.
Through my work at Cyronel Services, I focus on this intersection between the technical controls surrounding AI and the human behavior around its use. Before an agent is deployed, organizations should understand what it can access, what actions it can take, where human approval is required, how its activity will be monitored and whether employees are prepared to use it safely.
Ultimately, safe AI adoption is much easier to design into an organization from the beginning than to retrofit once people and processes have become dependent on autonomous systems.
Accountability Cannot Be Automated
Nikita Astionov's point comes back to a basic part of security, knowing what has access to your systems and what that access allows it to do. An agent that can read a document is one thing. An agent that can read the document, access an internal system and then take action is another. The difference lies in the permissions around it and the controls in place when its behavior falls outside the expected workflow.
Employees will also have to adjust to working alongside systems that can complete tasks with little intervention, particularly as familiarity can make an agent's actions feel routine even when they involve sensitive information or important business processes. Knowing when to question an automated decision will remain an important part of using the technology safely.
Related Articles
VAST Data and CrowdStrike Extend Cybersecurity to Enterprise AI Data
Inside the OpenAI-Hugging Face Security Incident Reshaping How AI Rivals Collaborate on Safety
Exclusive: Why AI Governance and Global Digital Cooperation Are Entering a Defining New Era
Related Articles


