
AI
Sep 16, 2026

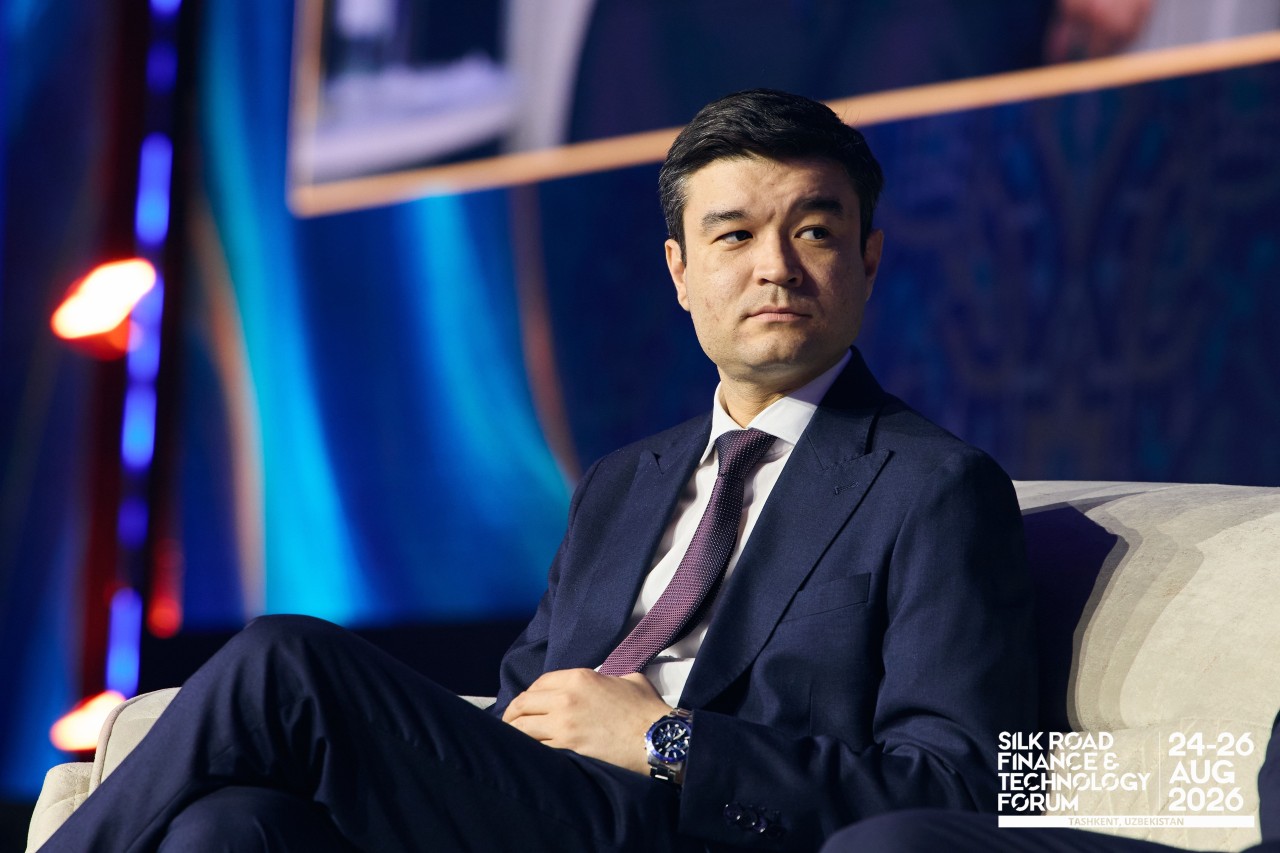
Sam Tayan is Regional Vice President, META at Illumio, leading sales strategy and regional growth across the Middle East, Türkiye, and Africa. With more than 30 years of experience in enterprise technology and cybersecurity, he has held senior roles at Zoom, Salesforce, Sage, VMware, Getronics, and Veritas Software.
[For more news, click here]
Enterprise AI is moving into a new phase. Copilots that once helped employees find information or complete tasks are increasingly giving way to autonomous agents capable of taking action across applications, systems, and data without constant human intervention. An AI agent can operate with legitimate permissions while making decisions and moving between systems at a speed that leaves little time for a human to intervene. As organizations give these systems greater autonomy, questions around identity, access, and accountability become harder to separate.
Critical infrastructure brings the issue into sharper focus. Operators cannot simply take essential systems offline whenever a vulnerability emerges, while organizations across the Middle East are connecting more services, applications, and data as digital transformation accelerates. More autonomous technology introduces another layer of complexity into environments where security and availability have to coexist.
Cybersecurity leaders are now having to think about more than keeping threats out. They are also dealing with what happens inside an environment when an authorized identity, compromised system, or autonomous agent begins behaving in ways that were not intended.
Tech Revolt spoke with Sam Tayan, Regional Vice President, META at Illumio, about the changing security landscape as organizations move deeper into the age of autonomous AI.
How AI Agents Are Changing Zero Trust
Q1. As enterprises move from AI copilots to autonomous AI agents that can take actions across systems, does “Zero Trust” need to evolve from verifying users and devices to continuously verifying what an AI agent is allowed to do?
Zero Trust has always been about continuous verification and least-privilege access, not just for people, but for any entity interacting with systems. As AI agents become more autonomous, they effectively become a new class of digital identity that must be governed accordingly. The challenge is that AI agents can operate at machine speed, access multiple systems simultaneously, and make decisions without constant human intervention. That makes containment even more important. Organizations need visibility into what AI agents can access, strict segmentation to limit their reach, and the ability to contain unintended behavior before it spreads across the environment. The principle of Zero Trust remains the same; the stakes are simply higher.
Q2. Critical infrastructure can't simply be taken offline or patched every time a vulnerability emerges. What have you learned from real-world deployments about containing attacks in environments where availability is more important than almost anything else?
One of the key lessons we've learned is that critical infrastructure organizations need to be able to reduce risk without changing how critical systems operate. In many environments, patching cycles are measured in months rather than days, and some systems simply can't be taken offline. As a result, the most successful organizations focus on understanding how systems communicate and limiting unnecessary connectivity. That allows them to reduce the attack surface and contain threats without disrupting essential operations, turning cybersecurity from a choice between security and availability into a way of achieving both.
Q3. What is the most interesting change you're seeing in customer behavior in the Middle East that you weren't seeing two or three years ago?
One of the biggest changes we've seen is the move from a prevention-first mindset to a resilience-first mindset. Organizations across the region continue to invest heavily in prevention and detection, but there's growing recognition that cyberattacks are inevitable, particularly as digital transformation and AI increase complexity. Government-led cybersecurity strategies and evolving regulations have helped accelerate that thinking by elevating cyber resilience to a business and national priority. As a result, customers are increasingly asking not just how to stop attacks, but how to contain them, protect critical assets, and maintain operations if a breach occurs. That focus on resilience wasn't nearly as prominent in conversations three years ago as it is today.
Q4. There's a lot of discussion around “cyber resilience,” but the term can mean almost anything. If you had to define cyber resilience using three measurable outcomes, what would they be?
Cyber resilience gets used in a lot of different ways, but for me, it comes down to three measurable outcomes. First, how quickly can you detect and understand an incident? Second, how effectively can you contain it and limit the impact on critical systems and data? And third, how quickly can you recover normal operations without significant business disruption? If organizations can consistently reduce detection time, limit the blast radius of an attack, and restore services quickly, they're demonstrating real cyber resilience rather than simply talking about it.
Q5. What are you seeing in the field today that is causing you to change your own view of where cybersecurity is heading?
The biggest thing is probably the fact that frontier AI is compressing timelines on both sides of cybersecurity. Defenders are deploying AI agents that can act across environments at unprecedented speed and scale, while attackers are using AI to accelerate reconnaissance, social engineering, and attack execution. The result is that security teams have less time to react when something goes wrong. That's why I believe containment will become increasingly important. As AI accelerates both innovation and risk, organizations need to assume breaches will happen and ensure they can limit the impact before it spreads.
The Growing Importance of Containment
The shift toward autonomous AI agents is changing how organizations think about access, identity, and containment. As these systems become more capable, security teams will need to understand not only what an agent is authorized to do, but also how its activity can be limited when something goes wrong.
Critical infrastructure, legacy environments, and essential services require security measures that reduce risk without disrupting the systems organizations depend on. Resilience in these environments is measured not only by whether an attack can be prevented, but by how quickly its impact can be understood, contained, and recovered from.
As AI accelerates activity on both sides of the cybersecurity equation, the time available to respond will continue to shrink. Organizations operating in that environment will need visibility into how systems interact, clear boundaries around access, and the ability to contain unexpected behavior before it becomes a wider operational problem.
Zero Trust will increasingly be measured not only by who or what can enter an environment, but by how effectively an organization can control what happens next.
Related Articles
Delinea Takes AI Agent Security Beyond Access
Related Articles